What you get
Information security governance and ISMS
A management system that runs your security programme, built on ISO/IEC 27001 and 27002: roles, policies, KPIs, risk ownership, reporting and control monitoring.
Contact Us
GRC Gravity is a boutique advisory and implementation partner for governance, risk and compliance in information security and AI. We find the risks that matter and turn requirements into governance that works day to day. We don't stop at advice: we build the frameworks, controls and evidence that prove it.
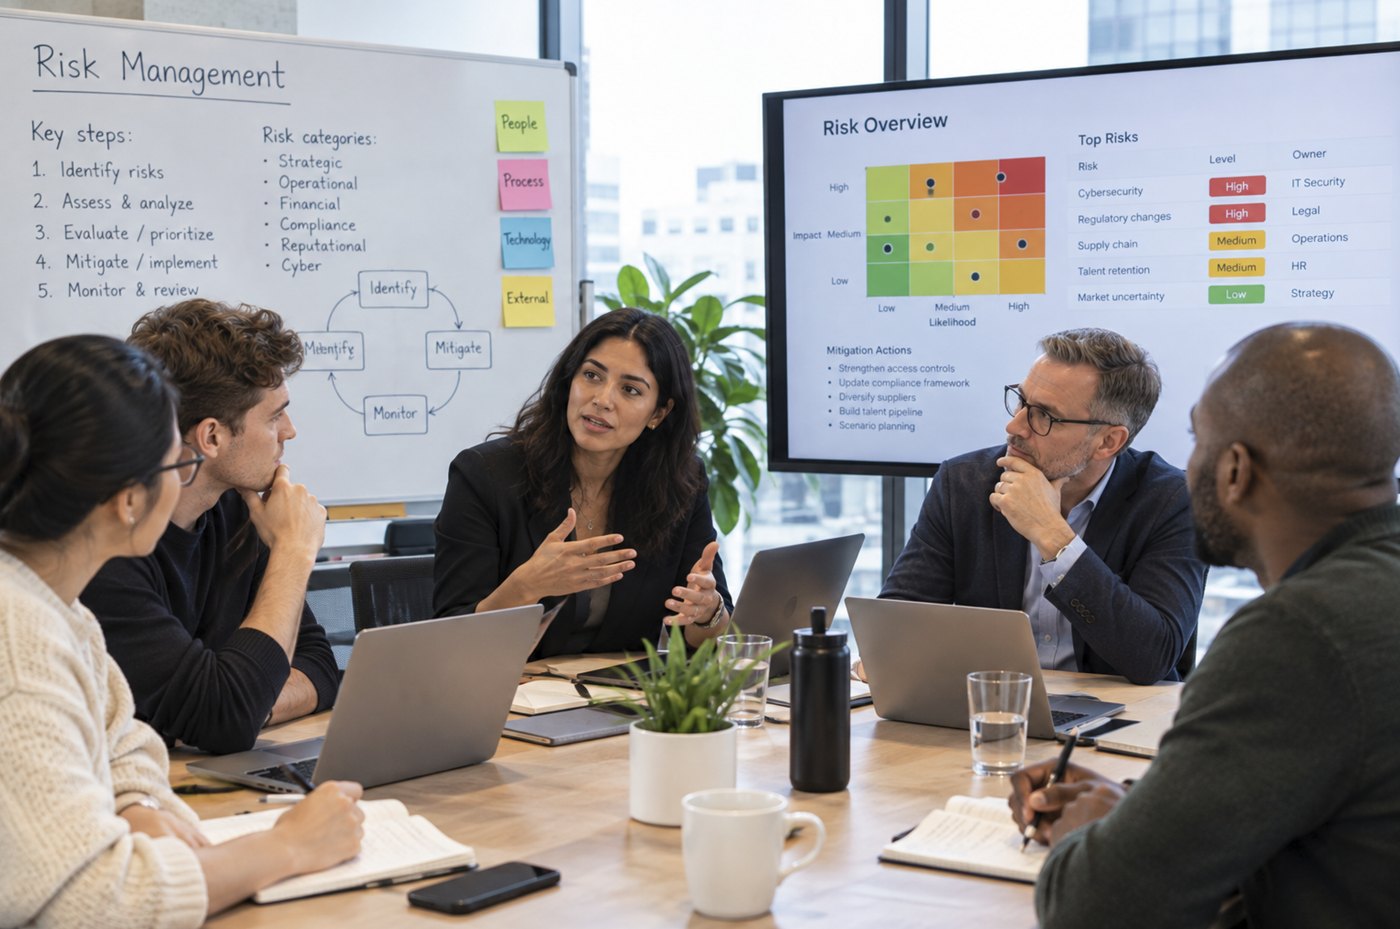
Risk overview
Illustrative
What you get
A management system that runs your security programme, built on ISO/IEC 27001 and 27002: roles, policies, KPIs, risk ownership, reporting and control monitoring.
What you get
See your risk clearly, inside and outside your organisation. Risk frameworks that cover the full lifecycle, extended to suppliers, cloud providers and outsourced services through third-party risk management.
What you get
Put responsible AI on a structured footing: governance, inventories, risk classification and lifecycle controls that support the EU AI Act and ISO/IEC 42001.
From requirements to evidence. We bring governance, risk, compliance, security, privacy, AI and third-party management together into one operating model, combining international standards with regulatory requirements.
Define the scope and ownership of processes, services and systems, then identify the risks, mitigations and risk owners.
Design and implement the frameworks, processes and controls, built on international standards.
Roles, responsibilities and ownership for every control and obligation.
Objectives, KPIs, control monitoring and management reporting.
Records that show your governance is working, for management, auditors, regulators and customers.
Practical
Fits how your organisation actually works.
Risk-based
Effort goes where the risk is.
Measurable
Objectives, KPIs and reporting that show performance.
Audit-ready
Evidence that holds up with auditors, regulators and customers.
We build AI governance and risk management frameworks that align with new regulation and recognised management-system principles, with compliance processes supporting the EU AI Act and ISO/IEC 42001.
Clear ownership for every AI system, with reporting to the board where it matters.
Know what you run and how much risk it carries, including the tools bought outside IT.
Control requirements, monitoring and documentation across the AI lifecycle, including AI from suppliers.
Example: one AI risk, managed
ISO/IEC 42001 and EU AI Act
System
CV screening in recruitment
Risk
The tool screens out candidates on grounds that would be unlawful if a recruiter applied them.
Mitigation
Human oversight after AI evaluation is mandatory. HR owns the documented process; evidence of compliance can be produced.
How the control is tested
PolicyAI-use procedure
DocumentationOperating and technical documentation
EvidenceOversight logs and review records
Frameworks, strategic plans and a board-level view of the control landscape.
NIST CSF 2.0, COBIT
The full risk lifecycle, extended to suppliers and other critical third parties.
ISO/IEC 27001, ISO 31000
Ready for the audit, and for the years after it.
ISO/IEC 27001, ISO/IEC 27701, ISO/IEC 42001, SOC 2
Inventories, classification, policies and controls, integrated with the ISMS.
ISO/IEC 42001, EU AI Act
From complex regulation to clear, repeatable routines.
GDPR, PCI DSS, NIS2, DORA, EU AI Act, EU CRA
Security operations centres, incident management and IT governance.
COBIT, NIST CSF 2.0
Frameworks and standards we work with
ISO/IEC 27001ISO/IEC 42001EU AI ActNIS2NIST CSF 2.0DORAGDPRCOBITSOC 2Both sides of the table: we have run security inside organisations and advised them from outside.
Chief Information Security and Governance Officer at a global energy trading company. Built the governance, risk and awareness programmes and established the security operations centre.
Led the information security and privacy practice at a Swedish consultancy, advising clients across financial services, healthcare, consumer goods, SaaS and energy.
We will come back with a proposed scope, a timeline and an honest view of the effort involved.
Office
Stockholm, Sweden